One model of your code and cloud
Every investigation starts with a live picture of your code, runtime, cloud, and controls.


Maze has made it feel like we have a team of security engineers that I can confidently rely on for triaging vulnerabilities.
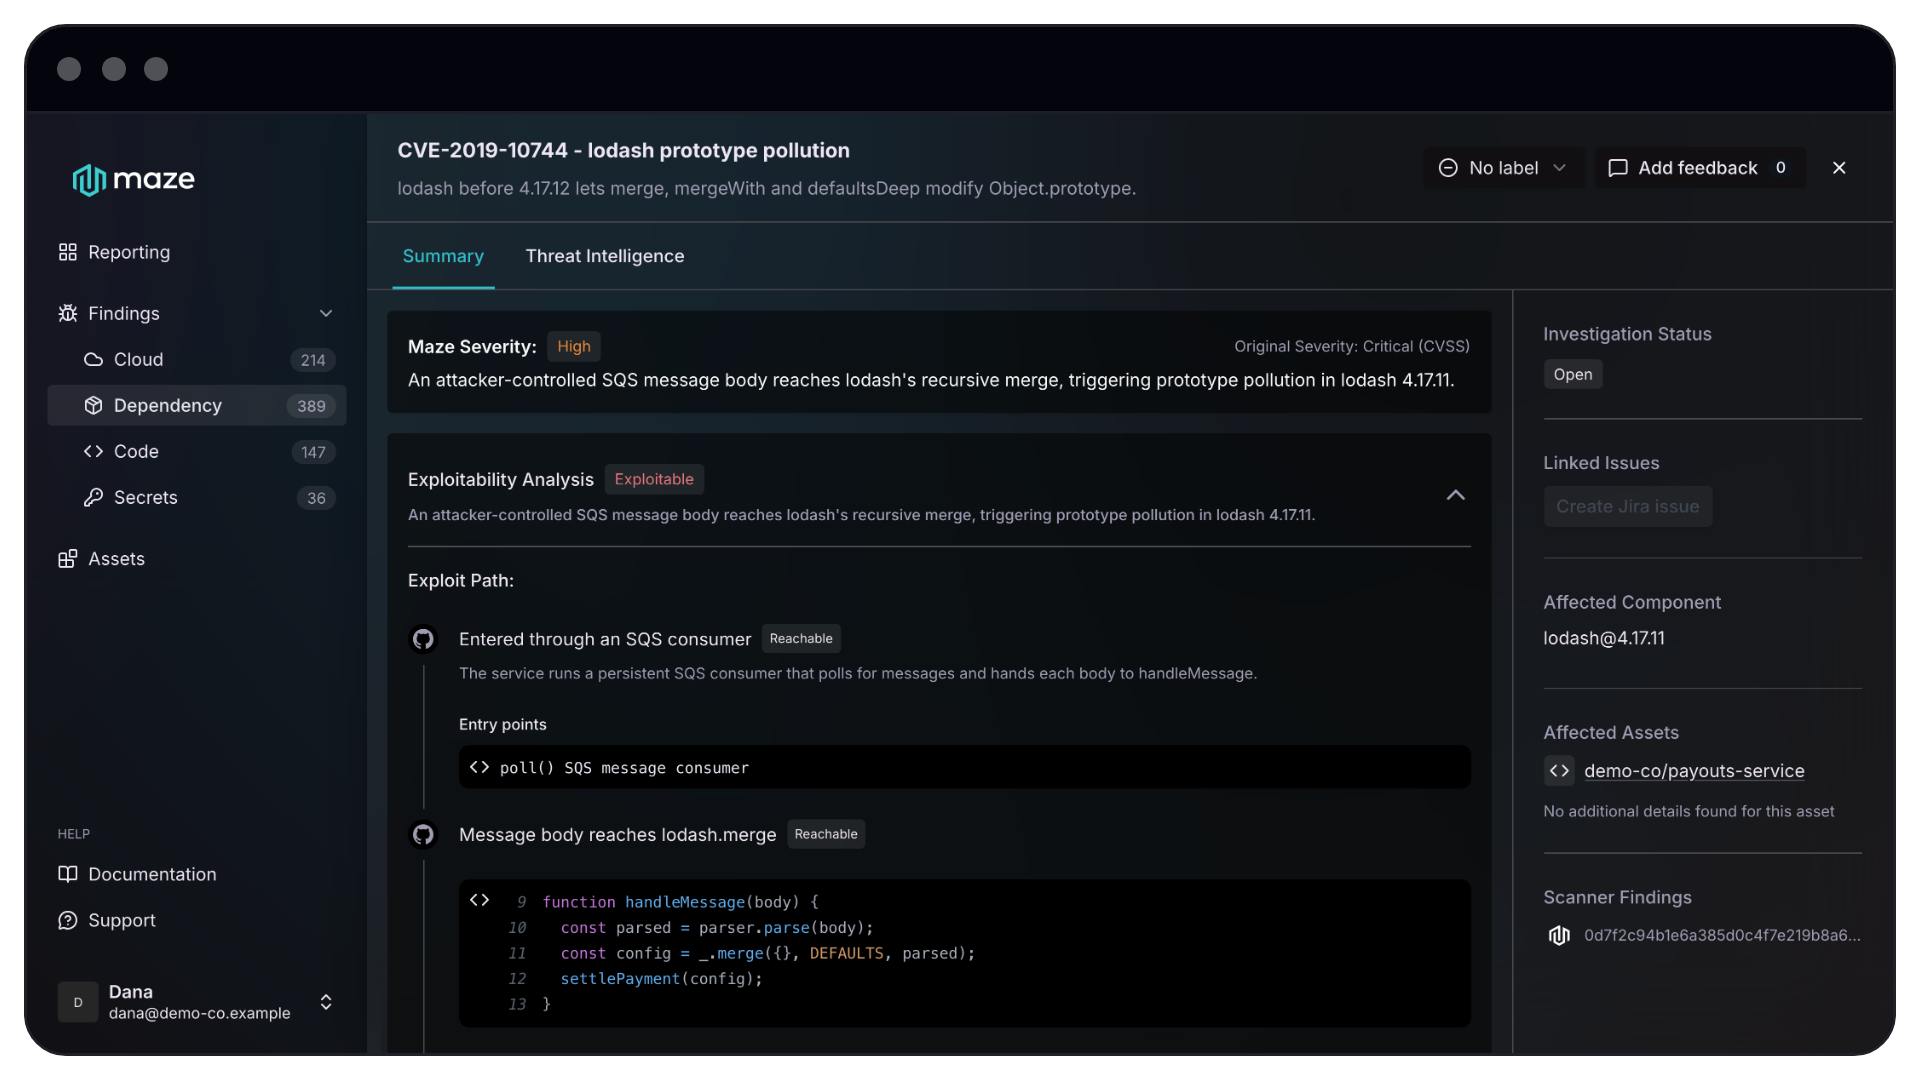
Every investigation starts with a live picture of your code, runtime, cloud, and controls.
Maze’s agents are trained on millions of real investigations, so each works like your best security engineer.
Multiple layers of validation catch errors as agents work, delivering results you can rely on.
You get a predictable price, and we handle the cost optimization while still running continuously.

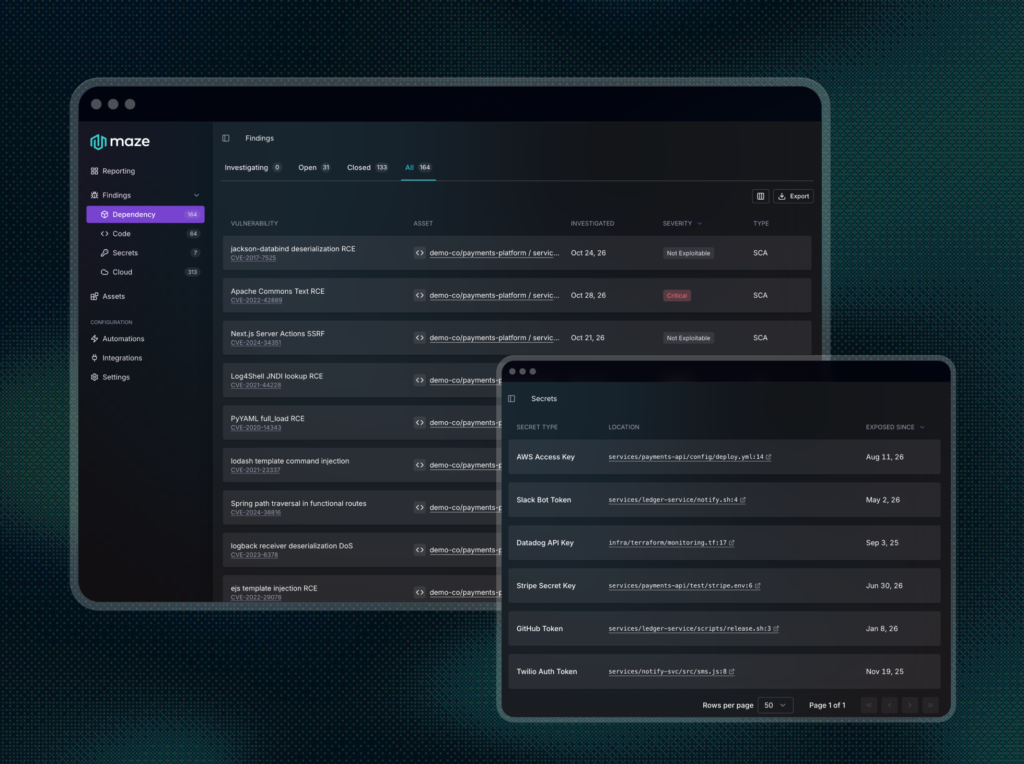
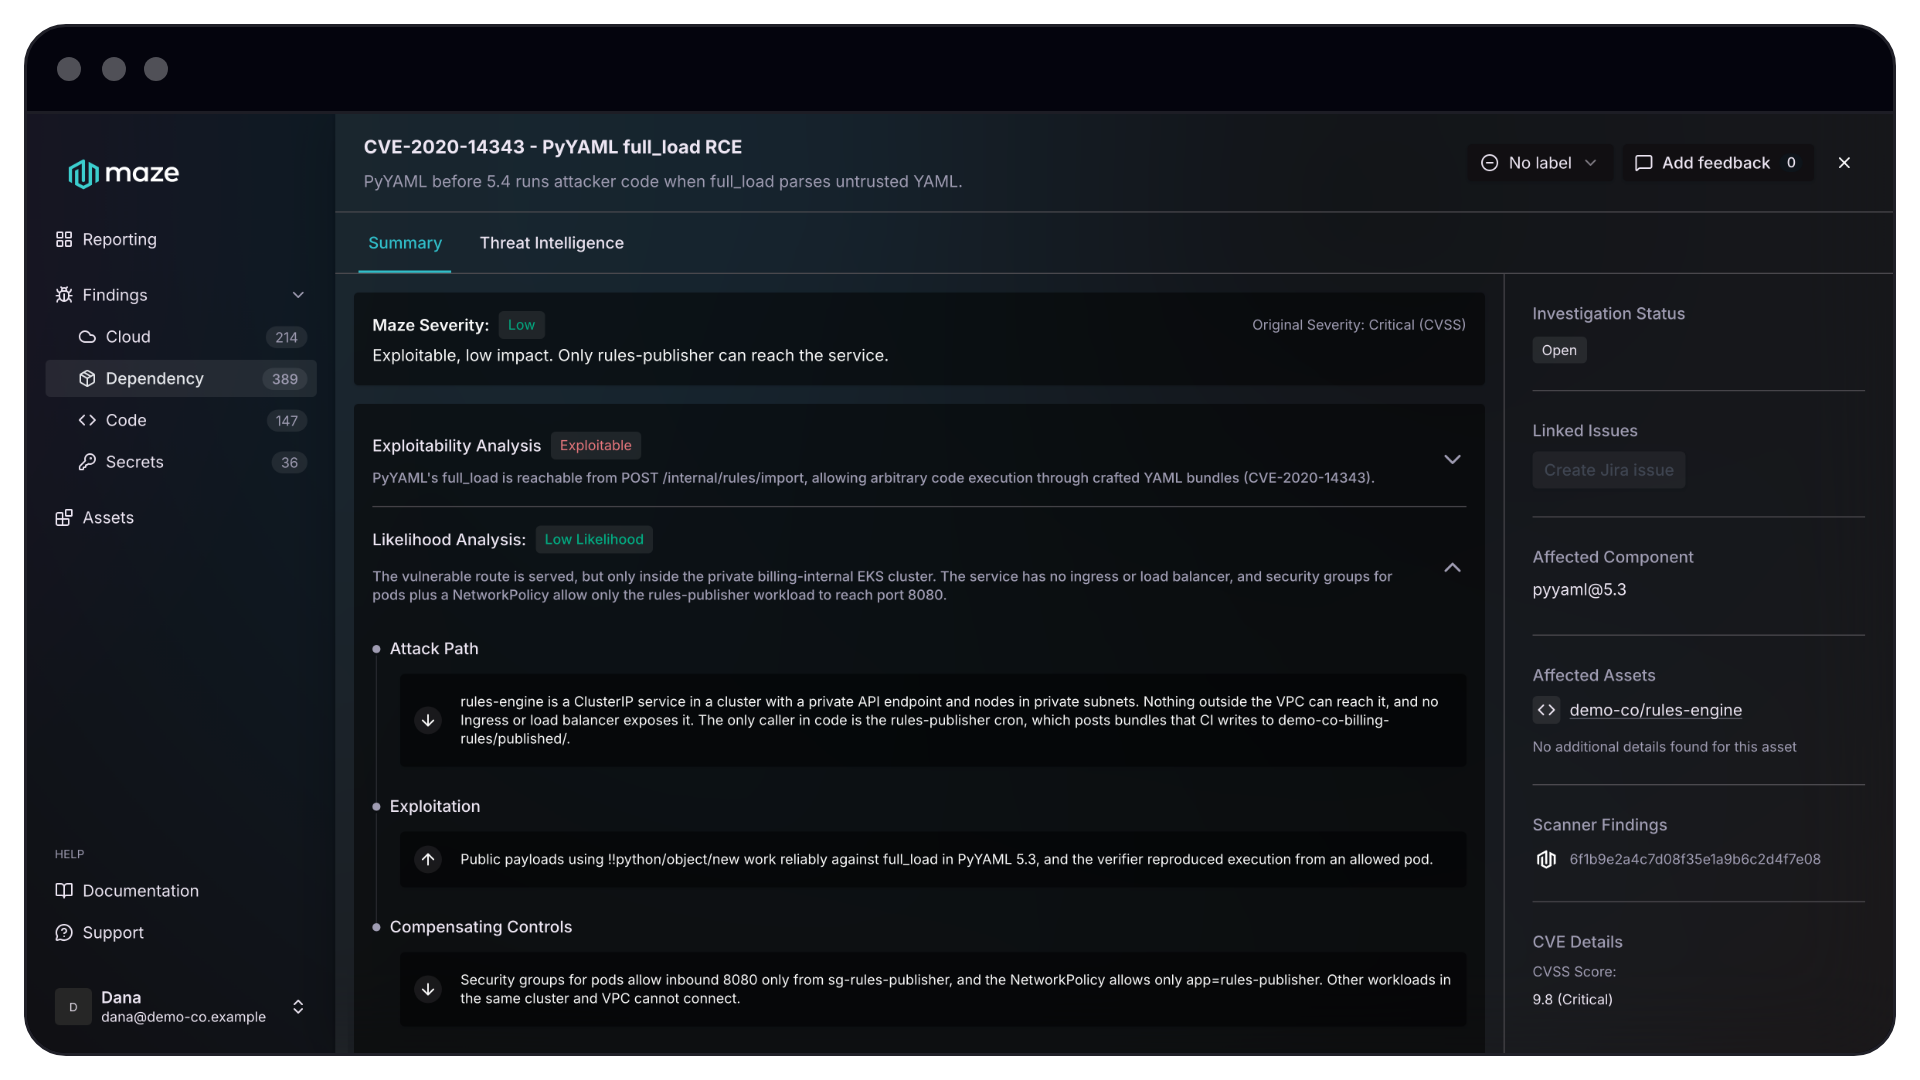
By combining context from code, cloud, and runtime, Maze investigates every finding, shows you what’s not exploitable, and prioritizes the rest.
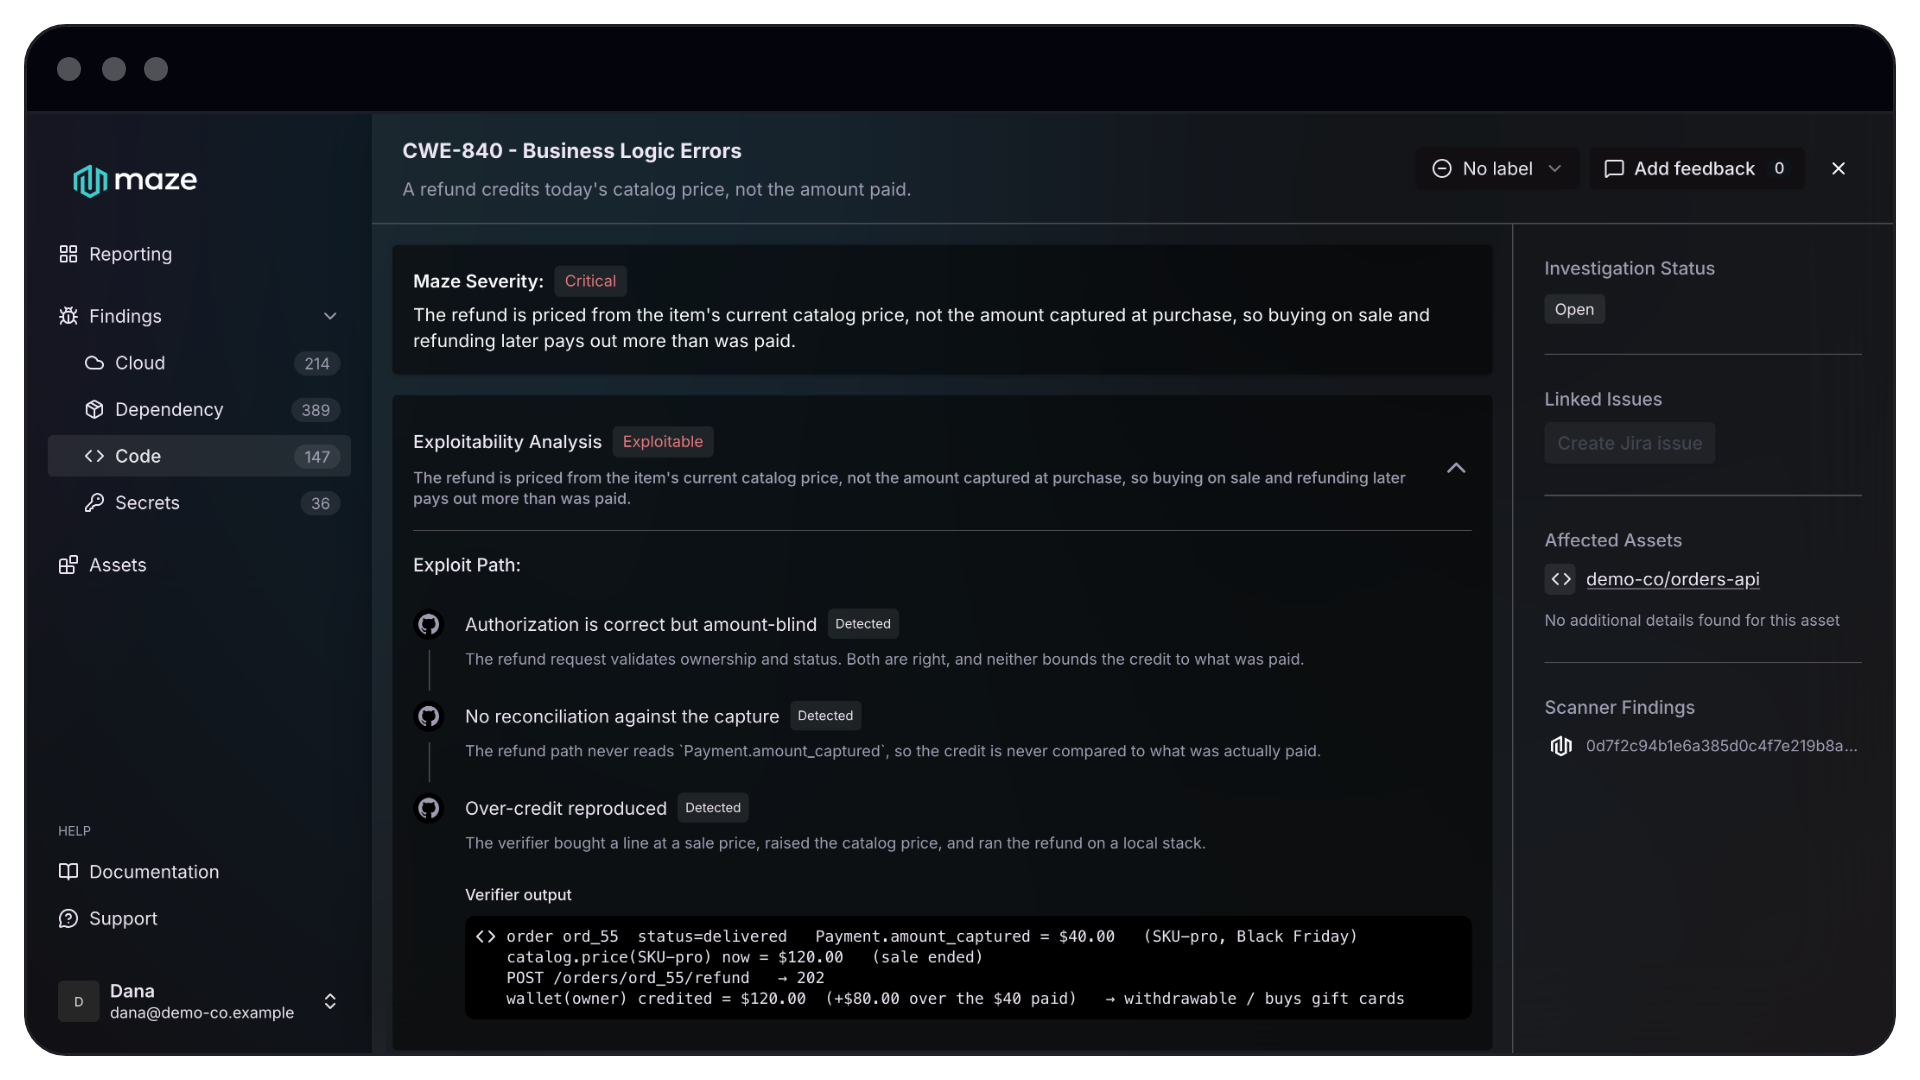
Maze’s agents build threat models of your applications, understand business logic, and find the subtle vulnerabilities you don’t know about yet.


Agents trace each vulnerability to its root cause, verify the fix, and send it to your coding agent or engineer.
Find and fix exploitable vulnerabilities in third-party code.
Find and fix business-logic flaws and other complex vulnerabilities traditional scanners miss.
Triage and remediate CVEs in containers and VMs, and catch zero-days before scanners see them.
Everyone uses AI now. What makes Maze different, and how is the platform built for AI agents?
Why we’re building Maze to be a security company that thinks differently.
Security research, blogs, video, and more from security leaders and the Maze team.