Cloud Vulnerabilities
Triage and remediate CVEs in containers and VMs, and catch zero-days before scanners see them.


Maze has made it feel like we have a team of security engineers that I can confidently rely on for triaging vulnerabilities.


The textbook fix rarely fits your team’s reality. Agents offer several options, from restructuring a component to rebuilding the image, so you choose what works.

Vulnerabilities shouldn’t be fixed one at a time. Agents bundle proven-exploitable CVEs into high-impact fixes, so one ticket can close 30 or more.

When patching isn’t an option, we suggest mitigations that break the exploitability chain while you work toward a permanent fix.
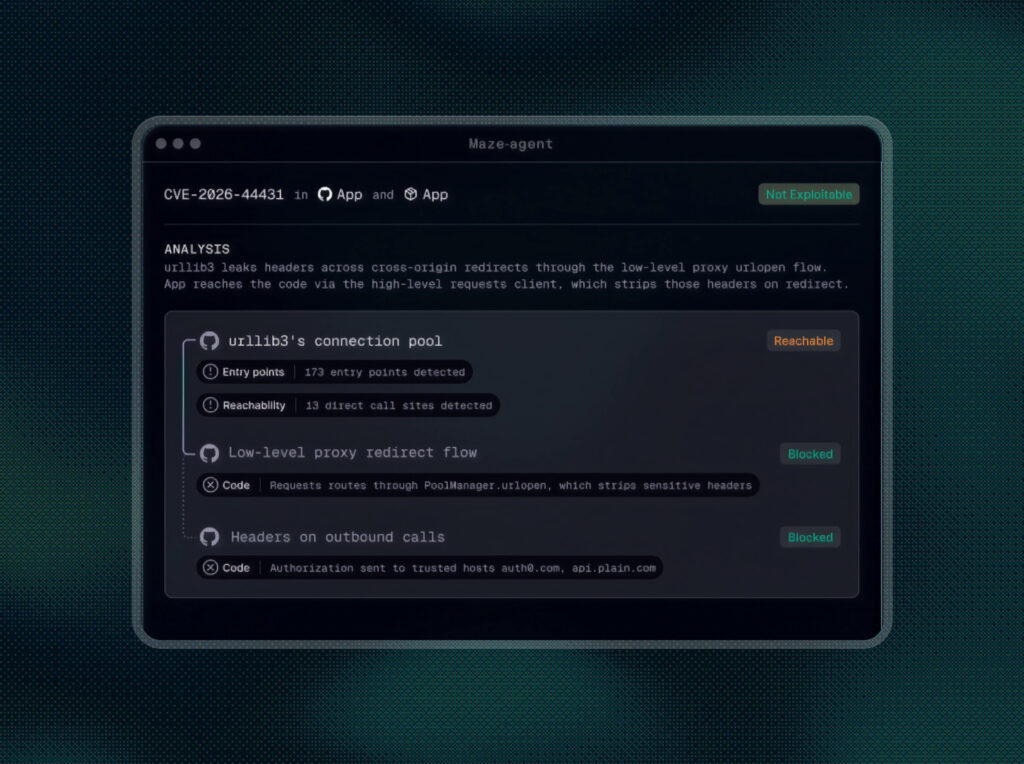
See how Maze AI agents find the root cause, validate a fix that works for your environment, and route it to the developer or coding agent that owns it.
See how Maze AI agents investigate and resolve cloud
vulnerabilities like your engineer would.
Remediation is part of both Maze Cloud and Maze Code. Wherever a vulnerability is proven exploitable, in your cloud, your code, or your dependencies, agents take it from verdict to a fix your team can ship. When patching isn’t an option, they recommend a mitigation instead.
Most tools hand you a list and wish you luck. Maze does the part after the list. Agents trace the root cause, write a fix validated for your environment, and deliver it to the person who can merge it.
Agents generate and validate fixes, then route them to the developer or coding agent that owns the code. Your team stays in control of what gets merged.
Nothing arrives as a black box. Every fix comes with the investigation behind it, what the vulnerability is, why the change resolves it, and the evidence for both. Your developers review and merge with full context, the same way they’d treat any PR.
Finding who owns the fix is often one of the harder problems. Agents gather context from your commit history, code, and more, then route it to the right developer or coding agent.
Fixes are routed to the responsible developer or coding agent through platforms like Jira.
Agents recommend a mitigation that makes the threat not exploitable, so the risk is handled even before a patch exists.
Yes. Agents bundle proven-exploitable CVEs into high-impact fixes, so a single change can close dozens of findings that share a root cause.
The textbook fix rarely accounts for your team’s reality. Agents propose several options, from a version bump to restructuring a component, so you pick the fix that matches your needs.
Deployment can be done in under five minutes. All we need is a read-only role in your cloud environment and an API connection to one or more vulnerability scanners.
We aim to keep pricing simple and fair. Large language models aren’t cheap, but we’ve worked hard to optimize cost and performance to make sure our pricing is reasonable.
Yes, Maze is cloud-hosted in AWS. Customers can choose between multi-tenant and single-tenant hosting.
Maze has been built for enterprise from day one. We have passed our ISO 27001 accreditation and are currently in our SOC 2 Type 2 observation window.
Triage and remediate CVEs in containers and VMs, and catch zero-days before scanners see them.
Find, triage, and remediate CVEs in third-party code, using your existing scanner or ours.
Find and fix business-logic vulnerabilities that SAST misses, or triage results from your existing scanner.
Everyone uses AI now. What makes Maze different, and how is the platform built for AI agents?
Why we’re building Maze to be a security company that thinks differently.
Security research, blogs, video, and more from security leaders and the Maze team.