Cloud Vulnerabilities
Triage and remediate CVEs in containers and VMs, and catch zero-days before scanners see them.


Maze has made it feel like we have a team of security engineers that I can confidently rely on for triaging vulnerabilities.


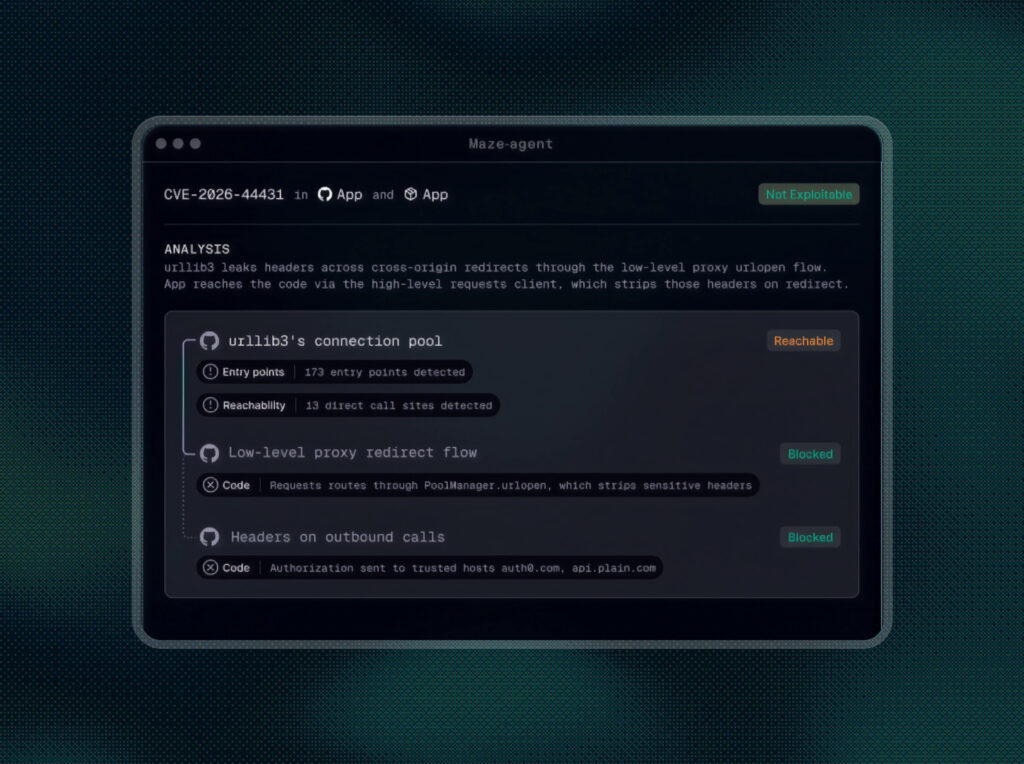
Maze agents determine exploitability, surfacing only true positives. Then they prioritize based on risk using context from your code, build, and runtime.

Agents apply a deep understanding of your code and cloud to every finding. They’re trained on millions of investigations and validated continuously.

Once Maze agents determine a finding is exploitable, they assess its blast radius and how realistic the attack is, using your context, so you know what to fix first.
Investigate every finding. Agents know when to reach for a frontier model and when to rely on a cost-efficient technique, so you can run them at scale.
See how Maze AI agents investigate, prove, and fix code
vulnerabilities the way your best AppSec engineer would.
See how Maze AI agents investigate and resolve cloud
vulnerabilities like your engineer would.
Think of it as an experienced security engineer reading your code. Maze agents understand every line, catch the vulnerabilities a rules-based scanner can’t, and clear the false positives that bury your team. Every finding is investigated to prove whether it’s exploitable, and the ones that matter arrive with evidence and a fix.
Your SAST tool matches patterns, and most of what it finds isn’t real. Maze agents read your code the way a security engineer would, so they find the flaws rules can’t describe and investigate every finding to prove what’s exploitable. Most turn out to be noise, and we show you why.
Yes. Maze Code scans both your code and your dependencies, so you don’t need a separate scanner to get started. It also integrates with the third-party scanners you already run, ingesting and deduping their findings and investigating them.
Yes. A rule can only describe a pattern someone has already seen. Maze agents understand what your code is meant to do, so they catch flaws in your business logic, like skipping a check, or letting one user act as another. No signature matches those.
An LLM is part of it, but on its own that isn’t enough. Maze agents gather the context a security engineer would want first, like the call graph, data flow, build, and runtime, and pick the right method for each step. The harnesses around the model are what make verdicts reliable.
Every verdict is grounded in evidence from your code and cloud. Nothing is a black box, so you can open any finding and see exactly why Maze reached that conclusion. Our agents are tested continuously by internal and external security experts to catch errors before you see them.
No. Maze Code works on its own, investigating every finding with context from your code and build. Add Maze Cloud and agents also see how that code runs in production.
Yes. Maze Code runs in your CI/CD pipeline (GitHub Actions, GitLab CI, CircleCI) and surfaces findings right at the pull request. Fixes route to the developer who owns the code or to the coding agents your team already uses.
Deployment can be done in under five minutes. All we need is a read-only role in your cloud environment and an API connection to one or more vulnerability scanners.
We aim to keep pricing simple and fair. Large language models aren’t cheap, but we’ve worked hard to optimize cost and performance to make sure our pricing is reasonable.
Yes, Maze is cloud-hosted in AWS. Customers can choose between multi-tenant and single-tenant hosting.
Maze has been built for enterprise from day one. We have passed our ISO 27001 accreditation and are currently in our SOC 2 Type 2 observation window.
Triage and remediate CVEs in containers and VMs, and catch zero-days before scanners see them.
Find, triage, and remediate CVEs in third-party code, using your existing scanner or ours.
Find and fix business-logic vulnerabilities that SAST misses, or triage results from your existing scanner.
Everyone uses AI now. What makes Maze different, and how is the platform built for AI agents?
Why we’re building Maze to be a security company that thinks differently.
Security research, blogs, video, and more from security leaders and the Maze team.